 dailynewsnblog
The cyberattack on French supermarkets earlier this week that ultimately spoiled hundreds of fridges worth of food should be a wake-up call about the vulnerabilities of digitized systems and devices that are connected to the internet, cybersecurity experts say.
“The more we rely on connected technology, the more we need to keep in mind the crucial aspect that is their security and privacy,” said Montreal-based cybersecurity expert Steven Lachance.
The attack appeared to target centralized control systems that allow the temperature of fridges to be changed remotely. Hackers were able to access those controls and jack up fridge temperatures at hundreds of grocery stores — in some cases as high as 50 C — causing their contents to spoil, and potentially causing fires.
The Paris prosecutor’s office said Tuesday that its cybercrime unit was investigating the large-scale attack to determine the extent of the damage and pin down the hackers behind it. No group has claimed responsibility so far, nor was there a ransom demand, according to Reuters.
Here’s what you need to know about the supermarket cyberattack and what it shows about the vulnerability of our tech — from commercial systems to household devices.
What happened in France?
Toronto-based tech and cybersecurity analyst Ritesh Kotak says the fridges in stores are usually connected to the internet through a centralized panel that allows metrics like temperature to be monitored and adjusted remotely.
Dominique Schelcher, CEO of Coopérative U, one of the affected French grocery store chains, said on social media that its fridges are connected to the internet in this way in order to monitor temperatures around the clock “in the event of an anomaly.”
On Monday, France’s national cybersecurity agency, ANSSI, said it was aware of numerous refrigerator control panels being compromised.
ANSSI said the remote monitoring systems targeted were made by a Dutch company called Danfoss. The cybersecurity agency later said similar systems made by Copeland and Dixell were also targeted.

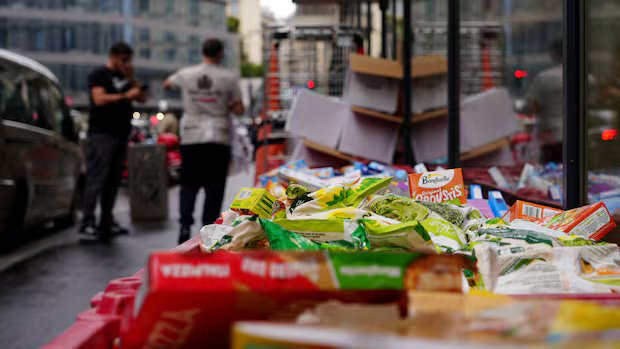
View of empty refrigerators at the frozen food aisle inside an Intermarché supermarket in Paris on Tuesday. The placard reads: “Important information. Our store has been hacked, and our refrigeration system has been affected.” (Lucien Libert/Reuters)
Danfoss told news agencies on Monday that the affected units were running “outdated firmware,” or had “reached end of life and no longer receive software or security updates.”
Cybersecurity firm Claroty published a report in August detailing a vulnerability with Danfoss’s firmware that could allow hackers to bypass the standard login process and gain access in order to make changes remotely. Danfoss released a patch to fix the vulnerability shortly afterwards and urged users to install it.
“These vulnerabilities should be considered serious,” the company said in its security advisory at the time.
The exact mechanism used to hack the fridge controllers in France is still unknown, but experts say it appears as though a failure to implement Danfoss’s updates, as well as interfaces being left open to the internet, enabled it.
Kotak says out-of-date firmware in particular would have made the hack easy to pull off.
Firmware updates are sent out once a vulnerability has been detected — so when customers are made aware they need to implement an update, hackers become aware of the problem, too.

A new EY report suggests AI will become a major force behind cybercrime in 2026 as programs help attackers hone their scamming skills.
“As a hacker, you will be able to know exactly what those vulnerabilities are and write code to exploit those exact vulnerabilities,” Kotak said.
For that reason, Kotak says, implementing security updates quickly is really important.
Are such attacks on the food system common?
French Finance Minister Roland Lescure told the country’s parliament on Tuesday that about 700 of the country’s 10,000 supermarkets were affected.
He said there was no risk to France’s food supplies but acknowledged the attack “touches the heart of our food security.”
But Kotak points out this is not the first such attack on the food distribution system. In 2021, for example, JBS — a major global supplier of meats — was hit by a cyberattack that temporarily shut down operations in Canada, the U.S. and Australia.
In 2025, United Natural Foods, Inc. — one of the biggest distributors of organic food — experienced an attack that led to significant shortages at Whole Foods.
Also Tuesday, Dutch supermarket giant Ahold Delhaize said it was working to restore systems it had shut down following a security incident that began on Sunday night — one the Dutch cybersecurity watchdog NCSC said it did not believe was linked to the French supermarket hack.
“This is something that unfortunately we’re going to see more of,” Kotak said. “What’s happened in France needs to be a wake-up call that we need to take this seriously.”

About 9,000 universities around the world, including in Canada, were hit by a cyberattack targeting the learning management platform Canvas. Schools are now scrambling to determine the extent of the compromised data.
The food system’s importance makes it a big potential target for an attack, he adds — and with processing, packaging and logistics becoming increasingly digitized, more possible avenues open up for hackers to try to gain access.
Kotak says helping food businesses become more digitally literate — so they employ safety-related updates and respond quickly when cyber incidents arise — is part of the solution.
“Cybersecurity … cannot be something that’s a checkbox exercise. It needs to be something that’s continuously being invested [in]” Kotak said.
What kind of devices are vulnerable?
Lachance, the Montreal-based expert, says the situation in France should serve as a reminder that any devices connected to the internet could in theory be hacked.
As internet connectivity becomes baked into more kinds of devices — both at a commercial level and a residential level with “smart” appliances, including thermostats, fridges, dishwashers and even lightbulbs — they can become vulnerable, he says.
“There is the convenience of this centralized control,” Lachance said. But, “the security vulnerabilities that come with them [are] a growing problem and I suspect it’s just going to become worse.”

Joel Reardon, associate professor of computer science at the University of Calgary, was on CBC News at 6 to discuss his findings.
Lachance says devices that can record audio and video pose the most obvious privacy risks. Hacks have already happened, including a situation where hackers took control of some Ring cameras and used the tech to harass homeowners.
But hackers might also try to infiltrate smart devices in order to harvest passwords, or to gain access to other devices on the same network, Lachance says.
He says a solution is simply steering clear of smart devices, or keeping them disconnected from the internet in cases where that connectivity isn’t necessary — especially in cheaper or lower-end devices, where he says security updates might not be prioritized by manufacturers.
For any devices that can record video or audio, Lachance recommends storing that data locally rather than making it accessible remotely.
“That’s just the door waiting to be … broken in,” he said.