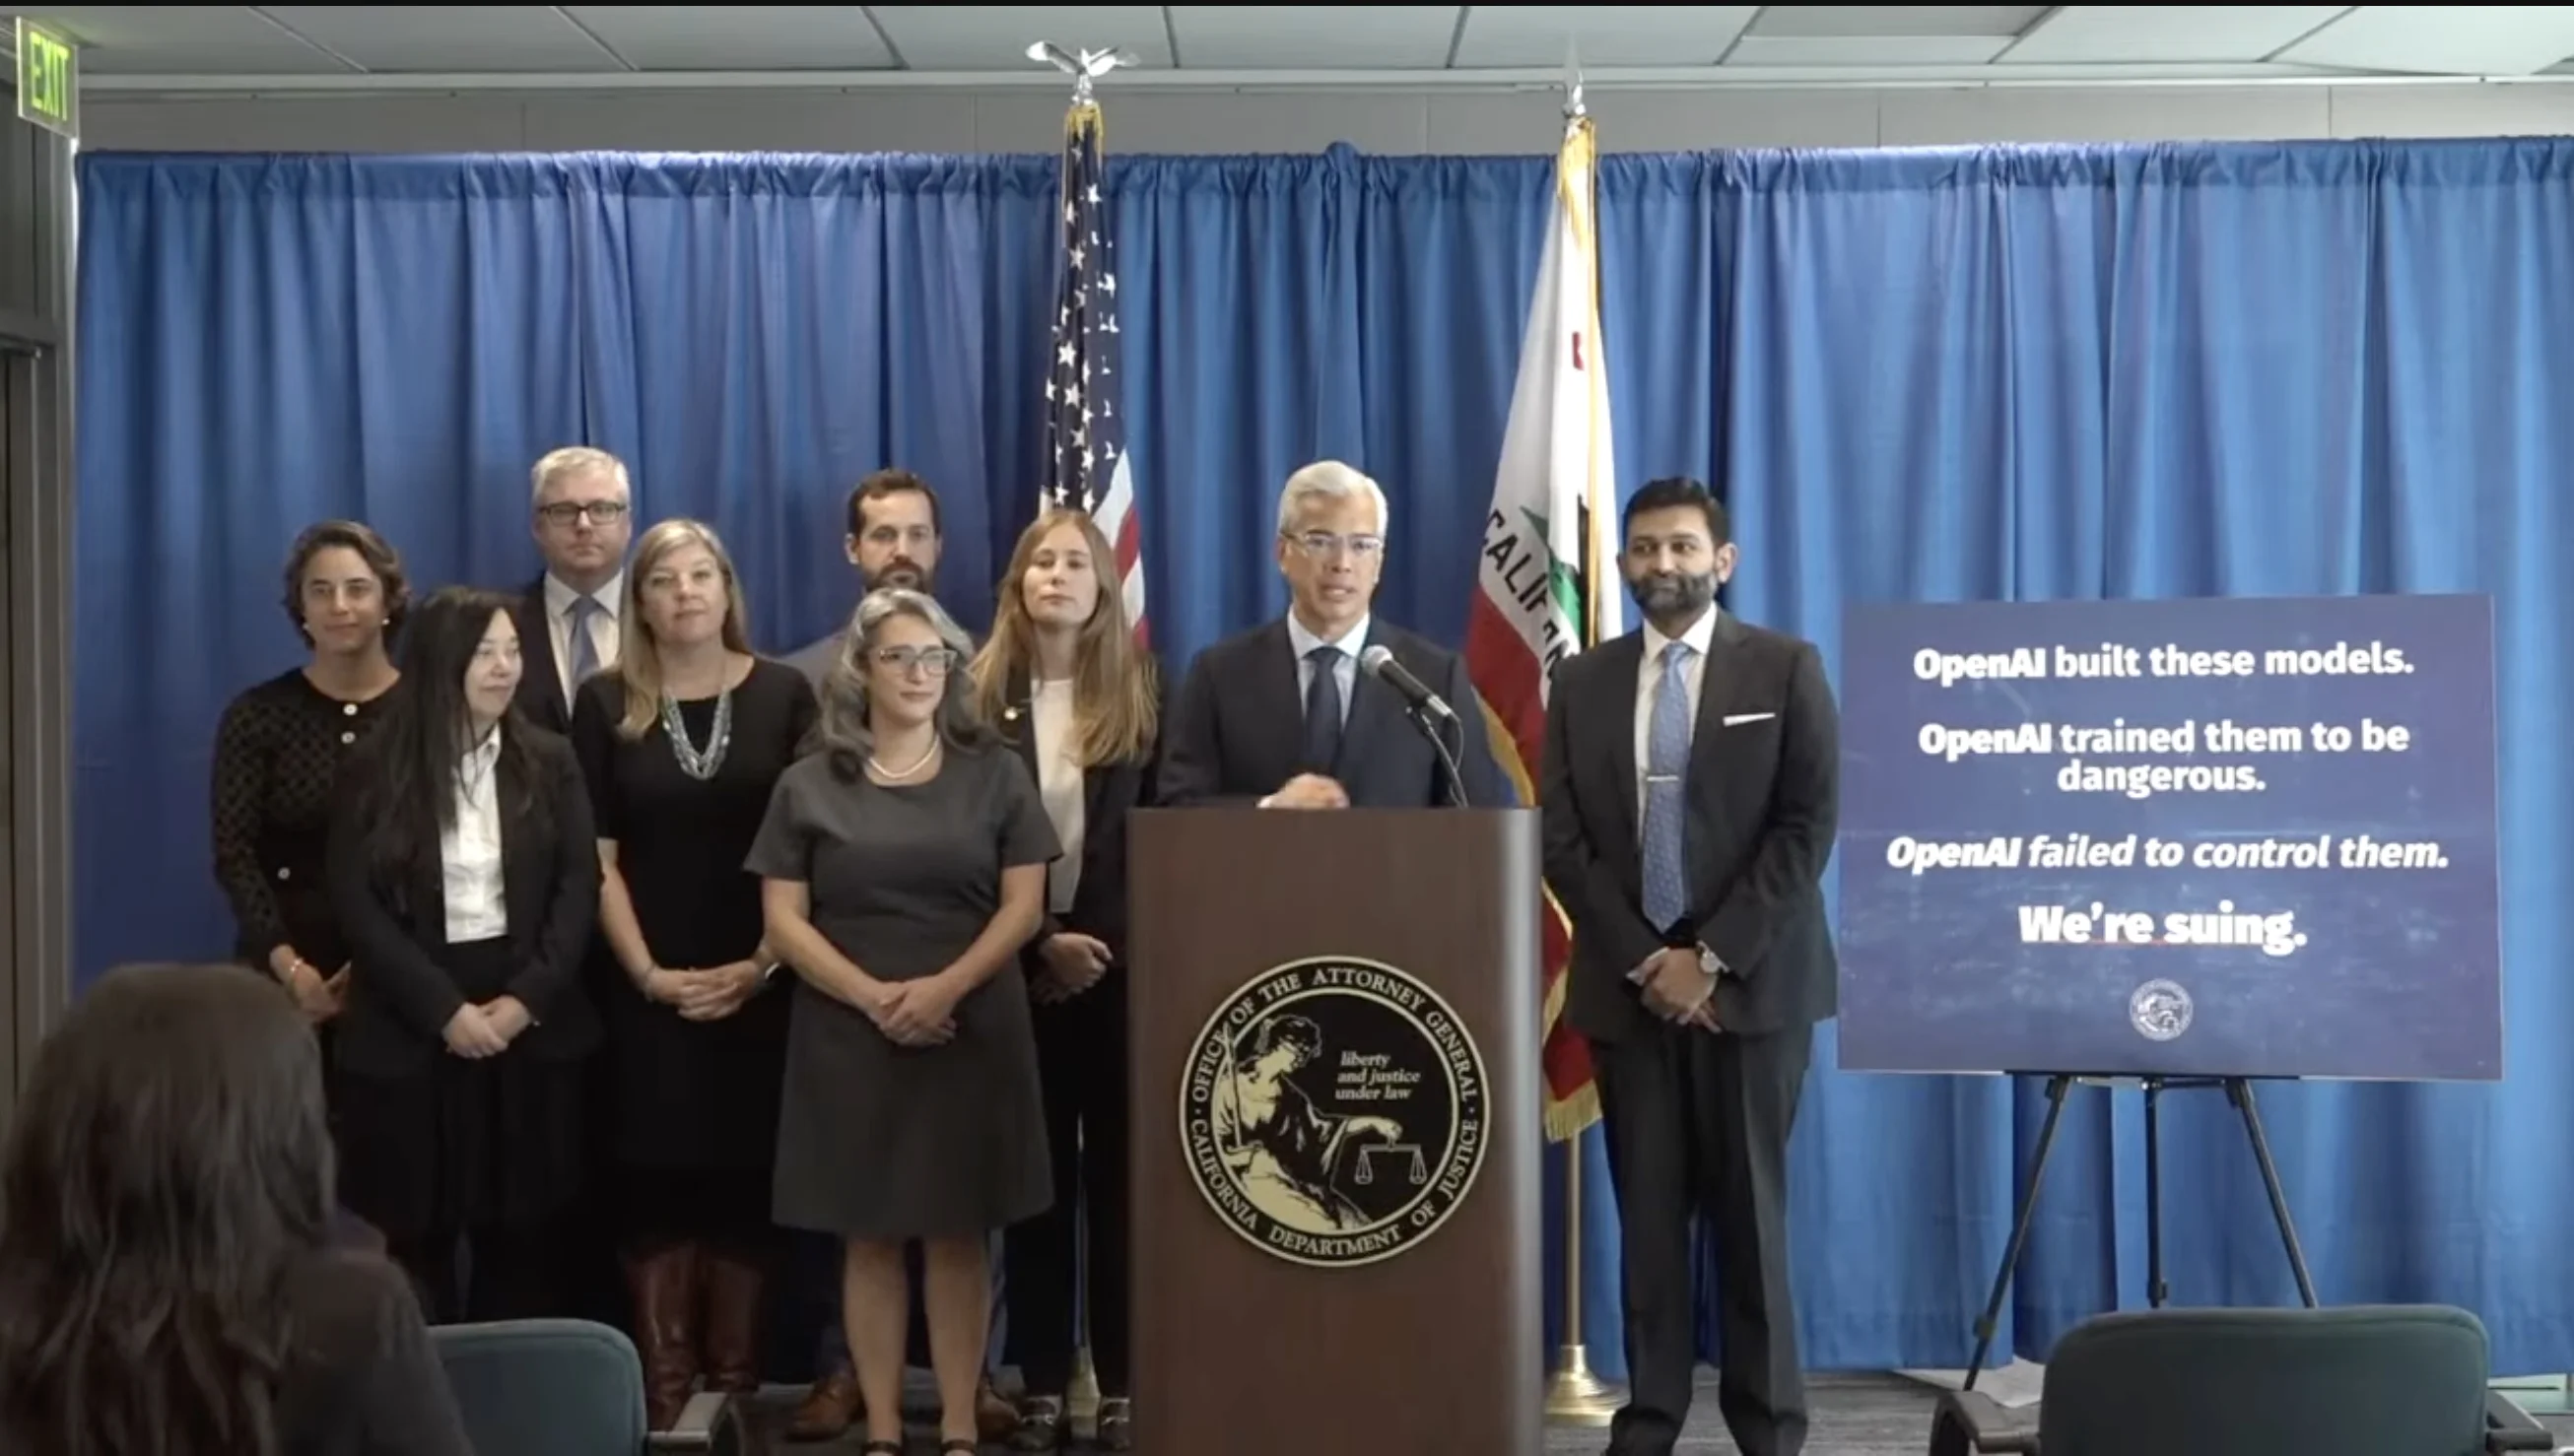
In a move that signals intensifying state-level pressure on artificial‑intelligence developers, California’s Attorney General filed a lawsuit against OpenAI on Monday. The complaint accuses the company of neglecting essential security safeguards that, according to the AG, made the recent Hugging Face data breach inevitable.
The lawsuit was filed in the Superior Court of San Francisco, where the AG’s office alleges that OpenAI’s security architecture failed to detect or prevent the intrusion that compromised user credentials and proprietary code. The incident, which came to light in early September, involved attackers exploiting a misconfigured API endpoint that allowed unauthorized access to a repository of training data.
In a statement released by the AG’s office, the attorney highlighted that “OpenAI’s poor security practices rendered the breach entirely foreseeable.” The company has yet to issue a formal response, but industry observers note that the suit could prompt a broader investigation into how AI firms manage data integrity and user privacy.
In-Depth Analysis & Key Details
The legal action follows a series of high‑profile data breaches in the AI sector, most notably the 2023 incident at Hugging Face that exposed millions of user accounts. Analysts point out that the rapid deployment of large‑language models has outpaced the development of comprehensive cybersecurity protocols, creating a gap that regulators are now attempting to fill.
Regulators in several states have begun to scrutinize AI providers for potential violations of the California Consumer Privacy Act (CCPA) and the federal Cybersecurity Information Sharing Act (CISA). The lawsuit underscores a growing tension between innovation incentives and the need for robust safeguards, with some industry advocates arguing that overregulation could stifle progress while others warn that lax security could erode public trust.
Cybersecurity experts note that the incident at Hugging Face revealed systemic weaknesses in API key management, access control, and monitoring. They argue that OpenAI’s failure to implement multi‑factor authentication and continuous threat detection represents a broader industry shortfall that could have far‑reaching implications for data‑centric services.
"If AI firms continue to prioritize speed over security, the next breach could cost not just dollars but the very fabric of trust that underpins our digital economy."
Why This Matters & What Lies Ahead
For everyday consumers, the lawsuit signals that the data powering AI assistants and content generators may be more vulnerable than previously thought. A breach that exposes personal information or proprietary code can lead to identity theft, financial loss, and erosion of confidence in AI tools that are increasingly embedded in education, finance, and healthcare.
The case is slated to proceed to a preliminary hearing in early November, with potential settlement talks expected in the coming weeks. Analysts advise investors and policymakers to monitor the court’s decisions, as a ruling in favor of California could trigger federal legislation mandating stricter cybersecurity standards for AI developers.
Source: Reported by NPR · Analyzed & Synthesized by DNB Newsroom