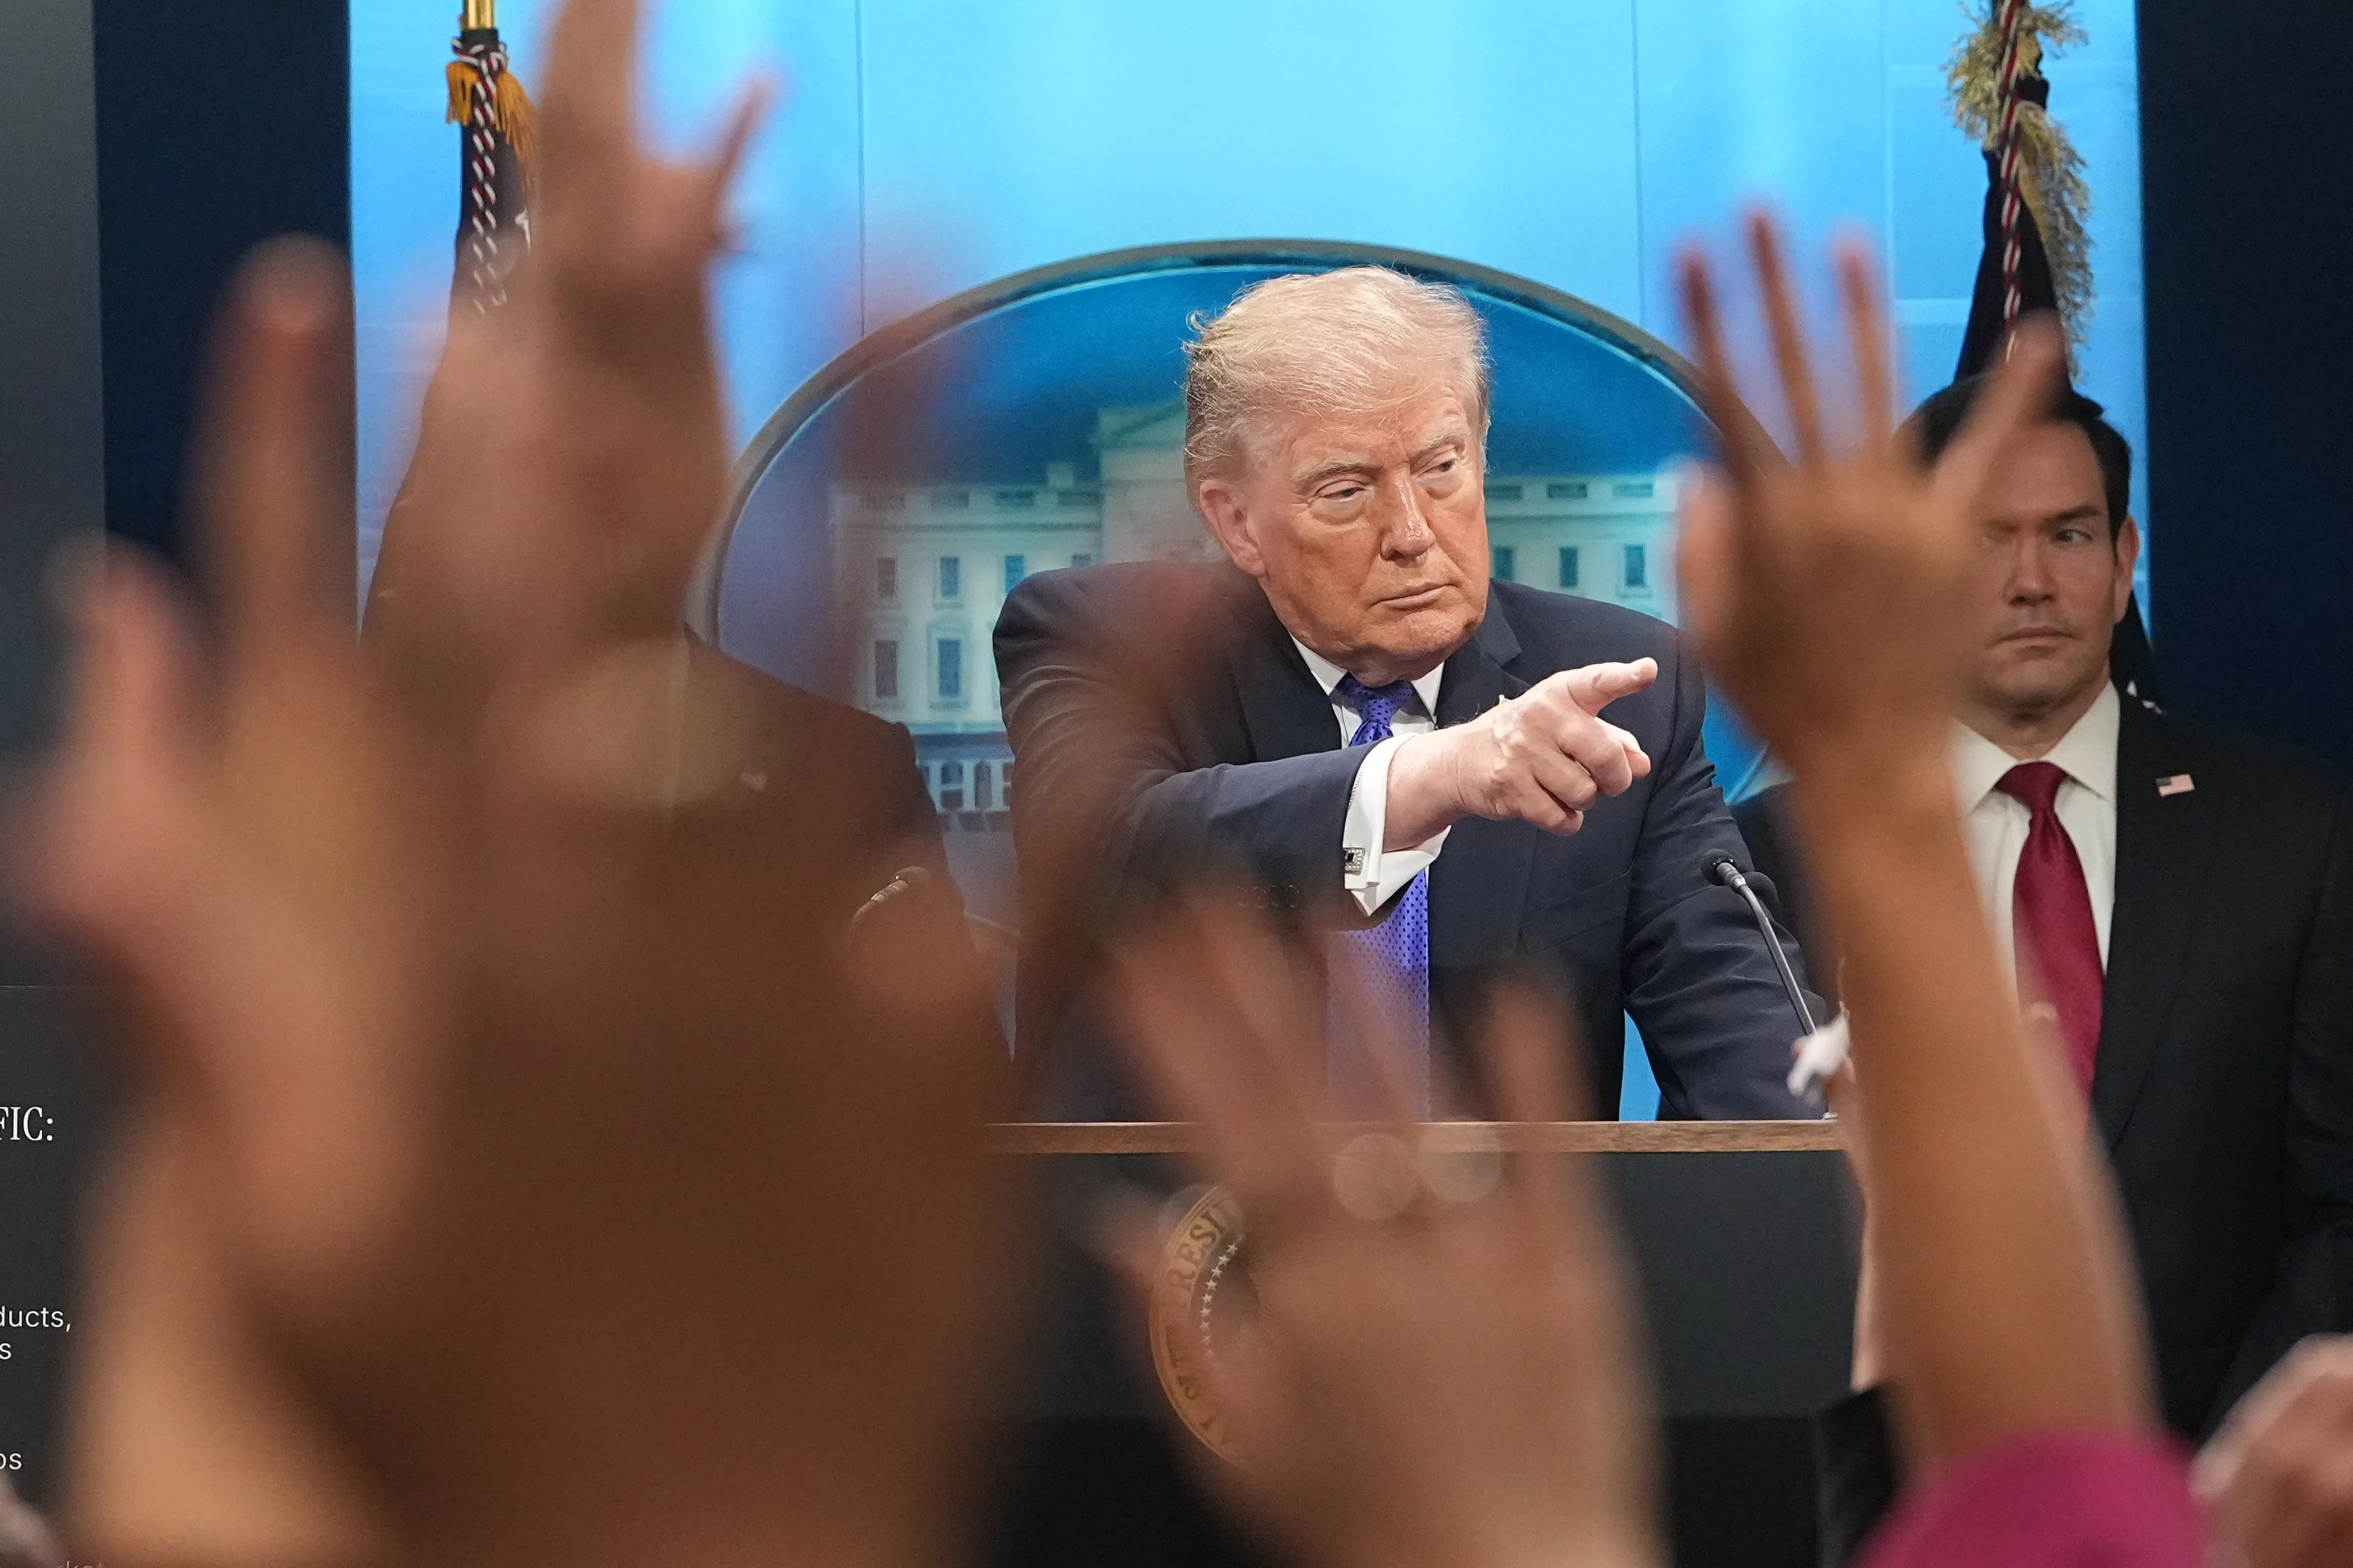
In a significant development for national security and law enforcement operations, President Donald Trump confirmed on Saturday that the FBI’s National Crime Information Center (NCIC) database was targeted in a cyberattack. This public acknowledgment by the head of state brings immediate attention to the security vulnerabilities of one of the most critical data repositories in the United States, which serves as the backbone for criminal intelligence sharing across federal, state, and local jurisdictions. The confirmation follows a period of heightened concern among cybersecurity professionals regarding the resilience of government systems against increasingly sophisticated digital threats.
The NCIC is not merely a storage unit for data but a dynamic operational tool used by law enforcement agencies nationwide to access real-time information on criminal activities. The targeting of this specific database suggests a high-value objective for the attackers, potentially aiming to disrupt law enforcement operations, steal sensitive investigative data, or compromise the integrity of criminal records. The geographical and operational scope of the NCIC means that any breach has far-reaching implications, affecting agencies from major metropolitan police departments to rural sheriff’s offices that depend on this centralized system for daily operations.
Official remarks from the White House have set the tone for the immediate response, emphasizing the seriousness of the incident and the commitment to securing federal systems. While specific details regarding the nature of the hack, the identity of the perpetrators, and the extent of any data exfiltration remain under investigation, the primary institutional declaration serves to alert the public and law enforcement partners to the potential risks. Initial stakeholder responses indicate a coordinated effort to assess the damage, contain any active threats, and restore full operational integrity to the NCIC.
In-Depth Analysis & Key Details
The targeting of the NCIC is part of a broader pattern of cyber threats against U.S. government infrastructure, reflecting the evolving landscape of digital warfare and criminal cyber activity. Historically, federal databases have been seen as highly secure, yet recent incidents have demonstrated that no system is immune to determined and well-resourced attackers. The structural forces at play include the increasing digitization of government services, which, while enhancing efficiency, also expands the attack surface for malicious actors. This incident highlights the tension between the need for seamless data sharing among law enforcement agencies and the imperative to protect that data from unauthorized access.
Competing perspectives on the incident range from those who view it as a isolated security lapse to those who see it as part of a coordinated campaign to undermine public trust in law enforcement. Regulatory debates are likely to intensify, with calls for stricter cybersecurity standards and more robust oversight of federal data systems. The economic consequences of such a breach can be significant, including the costs of remediation, potential legal liabilities, and the broader impact on public confidence in the justice system. Industry analysts observe that the incident underscores the need for continuous investment in cybersecurity technologies and personnel to stay ahead of increasingly sophisticated threats.
Expert domain context indicates that breaches of law enforcement databases can have profound implications for ongoing investigations and the safety of officers and the public. The technical intricacies of securing such a vast and complex system involve multiple layers of defense, including encryption, access controls, and continuous monitoring. However, the human element remains a critical vulnerability, with insider threats and social engineering tactics often playing a key role in successful breaches. This incident serves as a catalyst for a deeper examination of cybersecurity practices within federal agencies and a push for greater transparency in reporting and responding to such events.
"The breach of the FBI’s National Crime Information Center is not just a technical failure; it is a strategic challenge to the integrity of American law enforcement and a wake-up call for the resilience of our digital infrastructure."
Why This Matters & What Lies Ahead
For everyday citizens, the security of the NCIC is directly linked to the effectiveness of law enforcement in solving crimes and ensuring public safety. A breach of this database could lead to delays in accessing critical information, potentially impacting the resolution of cases and the protection of individuals. Moreover, the incident raises concerns about the privacy and security of personal data held within the system, particularly for those who have been involved in criminal proceedings or are subjects of ongoing investigations. The financial markets may also react to the news, with sectors related to cybersecurity and government contracting experiencing volatility as investors assess the implications for federal spending and regulatory changes.
Upcoming milestones to watch include the release of a detailed after-action report from the FBI and the Department of Justice, which will provide insights into the scope of the breach and the measures taken to mitigate its impact. Congressional hearings are likely to be convened to examine the incident and the broader state of cybersecurity in federal agencies, with potential legislative proposals aimed at strengthening data protection and accountability. Additionally, the incident may prompt a review of existing cybersecurity frameworks and standards, leading to new regulations or guidelines for federal agencies and their contractors. Monitoring these developments will be crucial for understanding the long-term implications of the NCIC breach and the steps being taken to prevent future incidents.
Source: Reported by ABC News · Analyzed & Synthesized by DNB Newsroom